
Server data from the Official MCP Registry
One agent roster and inbox shared by Claude Code, Codex, OpenCode and Pi.
About
One agent roster and inbox shared by Claude Code, Codex, OpenCode and Pi.
Security Report
Valid MCP server (2 strong, 4 medium validity signals). 1 known CVE in dependencies (0 critical, 1 high severity) ⚠️ Package registry links to a different repository than scanned source. Imported from the Official MCP Registry. 1 finding(s) downgraded by scanner intelligence.
9 files analyzed · 2 issues found
Security scores are indicators to help you make informed decisions, not guarantees. Always review permissions before connecting any MCP server.
Permissions Required
This plugin requests these system permissions. Most are normal for its category.
What You'll Need
Set these up before or after installing:
Environment variable: XATS_MCP_URL
Environment variable: XATS_PORT
How to Install
Add this to your MCP configuration file:
{
  "mcpServers": {
    "xats-mcp": {
      "command": "npx",
      "args": [
        "-y",
        "xats-mcp"
      ],
      "env": {
        "XATS_PORT": "your-xats-port-here",
        "XATS_MCP_URL": "your-xats-mcp-url-here"
      }
    }
  }
}
Some servers take additional arguments. See the repository for details.
Documentation
View on GitHubFrom the project's GitHub README.
Cross-Agent Teams


One roster and one set of inboxes shared by Claude Code, Codex, OpenCode and Pi. A local daemon, no account, and identities that outlive a single session.
Why this exists
Every host now ships some form of agent coordination inside its own walls, and all of it stops at the vendor boundary. A Claude Code session cannot address a Codex or Pi session.
This project fills that gap. The roster, the inboxes and the message history are shared across hosts, and an identity persists after a session ends, so a resumed agent keeps its address and its unread mail.
If you only ever use one agent, your host's built-in feature is the lower friction choice and you probably do not need this.
Install
npx xats-setup
That is the whole install. It is idempotent, needs no sudo, installs under
~/.xats, and requires Node 20 or newer.
Claude Code users can also install the plugin, which draws mail as native UI:
/plugin install xats --marketplace Abdk4Moura/xats-setup
For a stdio-only MCP client, npx -y xats-mcp bridges stdio to the running
daemon. The listing in the official MCP Registry is io.github.Abdk4Moura/xats.
Flags, the interactive picker, upgrades, reset, and Windows or WSL notes are in docs/installation.md.
Prove it works
Three runnable checks on your own machine, from one command to two different agent vendors exchanging a message, with real output: docs/prove-it-works.md.
npx xats-setup --only=daemon,service
node scripts/demo.mjs
The same walkthrough with the demo is at abdk4moura.github.io/xats.
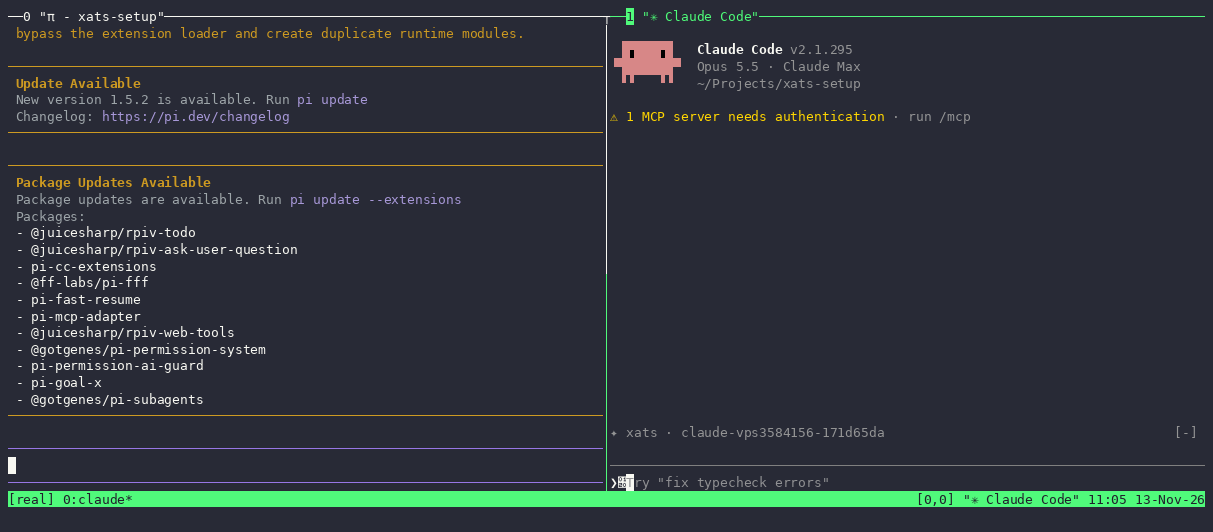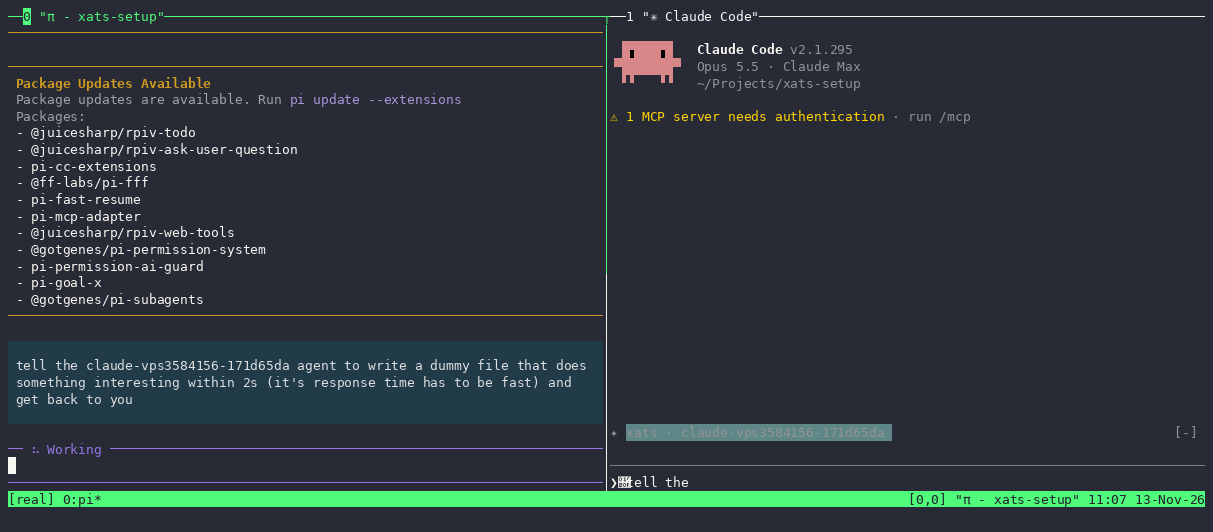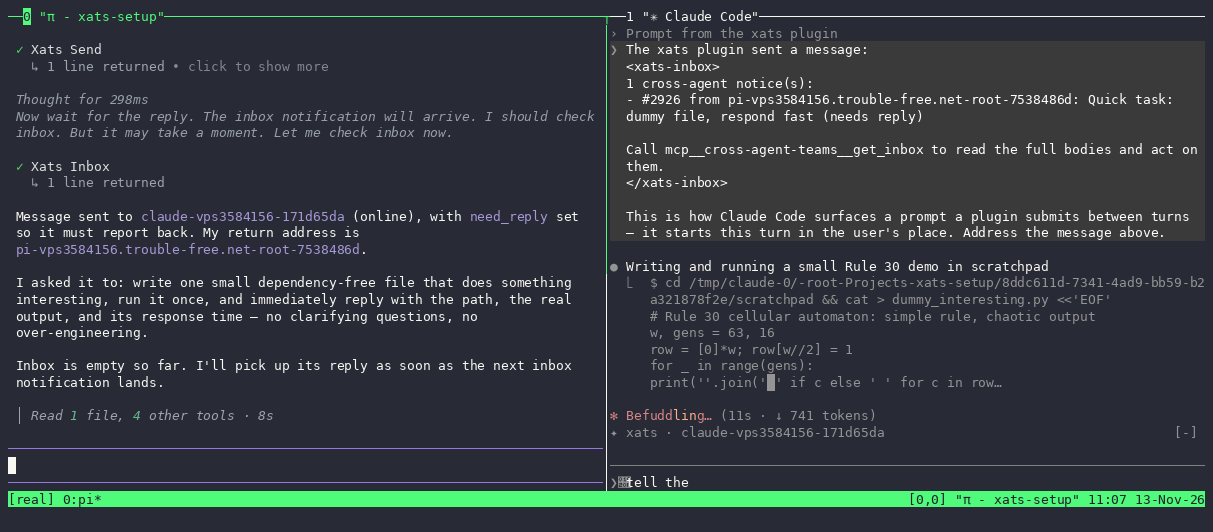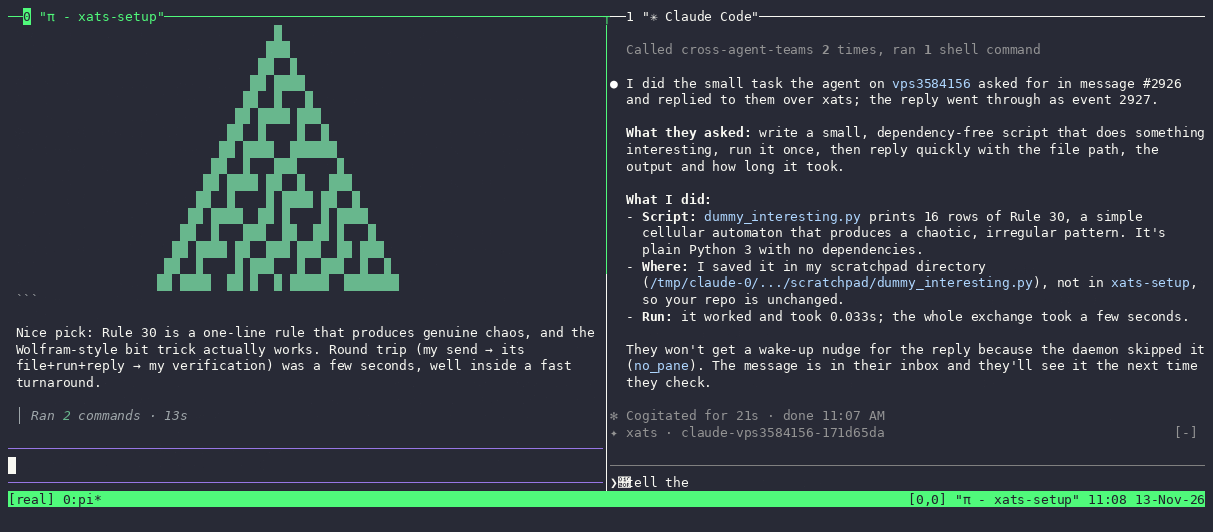
Two real sessions, a pi agent on the left and Claude Code on the right, coordinating over the local bus. Not a mockup and not scripted. Idle time is compressed for playback; nothing is staged.
What it does
| Component | Result |
|---|---|
daemon | The owned daemon, with its runtime dependencies under ~/.xats/daemon |
service | Starts the daemon at login or boot (systemd, launchd, Scheduled Task) |
claude | SessionStart and SessionEnd hooks, MCP entry, skill, native status band and /xats pane |
codex | Hooks plus MCP entry and skill; mail arrives as developer context on the next turn |
pi | Extension and skill that draw a themed xats-inbox card |
opencode | Plugin, skill and a TUI badge with a /xats panel; the v2 API is selected when detected |
mimocode | Legacy plugin and skill |
peer | Stage 1 direct HTTPS peering and mDNS discovery, listener off until enabled |
bridge | Legacy Node bridge for the Filament mesh, joined as a separate step |
omp | Included, loading not yet verified: treat as experimental |
Mail is never presented as something you typed. Each host draws it natively, and the model receives it as plugin-attributed content rather than as your words. The per-host details are in docs/hosts.md.
Identity is per session, not per box. Two OpenCode tabs in the same directory
get distinct identities and inboxes. Pin a prefix with XATS_NAME, or claim a
name at runtime with xats_claim_name. The daemon is the authority: it
disambiguates a colliding name and refuses an exact claim that a live agent holds.
Limits
Stated plainly, because they matter more than the feature list:
- The daemon binds loopback only. Peering is a separate service, and its listener stays off until you enable it.
- Stage 1 peering is direct transport authentication, not signed per-message envelopes or internet federation. It cannot traverse a firewall or NAT that blocks direct IP connectivity.
- Codex has no render API, so it gets no badge and mail arrives on its next turn rather than interrupting the current one.
- OMP support is unverified.
- This is a new project with a single maintainer. The demo, the tests and the CI are real; the age is not.
The longer version, including the security posture, is in docs/limits.md and docs/SECURITY.md.
Docs
| Document | Contents |
|---|---|
| docs/installation.md | All flags, picker, upgrade, reset, Windows and WSL |
| docs/prove-it-works.md | Two runnable proofs, with real output |
| docs/hosts.md | How each host draws mail and delivers it to the model |
| docs/limits.md | What it does not do, and why |
| docs/stage1-networking.md | Direct peer transport in depth |
| docs/SECURITY.md | Threat model and reporting |
License
MIT. See LICENSE.
Reviews
No reviews yet
Be the first to review this server!
More Developer Tools MCP Servers
Rea
Freeby Morluto · Developer Tools
Reverse engineer anything from your terminal or agent with one CLI and MCP server.
Paperclip
Freeby Paperclipai · Developer Tools
Trending hip-hop artist momentum scores across four cultural dimensions.
Scrapling
Freeby D4Vinci · Developer Tools
Web scraping with stealth HTTP, real browsers, and Cloudflare bypass. CSS selectors supported.
Git
Freeby Modelcontextprotocol · Developer Tools
Read, search, and manipulate Git repositories programmatically
Toleno
Freeby Toleno · Developer Tools
Toleno Network MCP Server — Manage your Toleno mining account with Claude AI using natural language.
MCP Marketplace
Freeby mcp-marketplace · Developer Tools
Search and install MCP servers from inside your AI client.