
Server data from the Official MCP Registry
Manage Keycloak users, groups, roles and realms through the Keycloak Admin REST API.
About
Manage Keycloak users, groups, roles and realms through the Keycloak Admin REST API.
Security Report
Valid MCP server (2 strong, 2 medium validity signals). No known CVEs in dependencies. Package registry verified. Imported from the Official MCP Registry. Trust signals: 4 highly-trusted packages.
10 files analyzed · 1 issue found
Security scores are indicators to help you make informed decisions, not guarantees. Always review permissions before connecting any MCP server.
Permissions Required
This plugin requests these system permissions. Most are normal for its category.
What You'll Need
Set these up before or after installing:
Environment variable: KEYCLOAK_URL
Environment variable: KEYCLOAK_AUTH_REALM
Environment variable: KEYCLOAK_CLIENT_ID
Environment variable: KEYCLOAK_CLIENT_SECRET
Environment variable: KEYCLOAK_USERNAME
Environment variable: KEYCLOAK_PASSWORD
Environment variable: KEYCLOAK_GRANT_TYPE
Environment variable: KEYCLOAK_MCP_READ_ONLY
Environment variable: KEYCLOAK_MCP_REALMS
Environment variable: KEYCLOAK_MCP_ALLOW_MASTER_WRITE
Environment variable: KEYCLOAK_MCP_TOOLSETS
Environment variable: KEYCLOAK_MCP_REQUIRE_CONFIRMATION
Environment variable: KEYCLOAK_MCP_TIMEOUT_MS
Environment variable: KEYCLOAK_MCP_LOG_LEVEL
How to Install
Add this to your MCP configuration file:
{
  "mcpServers": {
    "io-github-christophenglisch-keycloak-model-context-protocol": {
      "env": {
        "KEYCLOAK_URL": "your-keycloak-url-here",
        "KEYCLOAK_PASSWORD": "your-keycloak-password-here",
        "KEYCLOAK_USERNAME": "your-keycloak-username-here",
        "KEYCLOAK_CLIENT_ID": "your-keycloak-client-id-here",
        "KEYCLOAK_AUTH_REALM": "your-keycloak-auth-realm-here",
        "KEYCLOAK_GRANT_TYPE": "your-keycloak-grant-type-here",
        "KEYCLOAK_MCP_REALMS": "your-keycloak-mcp-realms-here",
        "KEYCLOAK_MCP_TOOLSETS": "your-keycloak-mcp-toolsets-here",
        "KEYCLOAK_CLIENT_SECRET": "your-keycloak-client-secret-here",
        "KEYCLOAK_MCP_LOG_LEVEL": "your-keycloak-mcp-log-level-here",
        "KEYCLOAK_MCP_READ_ONLY": "your-keycloak-mcp-read-only-here",
        "KEYCLOAK_MCP_TIMEOUT_MS": "your-keycloak-mcp-timeout-ms-here",
        "KEYCLOAK_MCP_ALLOW_MASTER_WRITE": "your-keycloak-mcp-allow-master-write-here",
        "KEYCLOAK_MCP_REQUIRE_CONFIRMATION": "your-keycloak-mcp-require-confirmation-here"
      },
      "args": [
        "-y",
        "keycloak-model-context-protocol"
      ],
      "command": "npx"
    }
  }
}Documentation
View on GitHubFrom the project's GitHub README.
Keycloak MCP Server


A Model Context Protocol (MCP) server for Keycloak administration. It lets an AI assistant such as Claude manage users, groups, roles and sessions, and inspect clients, events and the security posture of your realms, through the Keycloak Admin REST API, with least-privilege authentication and guardrails around every write.
[!WARNING] This server acts with the permissions of the Keycloak account you give it. Use a dedicated service-account client with only the roles you need, never the bootstrap admin. Destructive tools ask for confirmation by default, and a read-only mode is available. See Security.
Highlights
- 24 tools in 7 toolsets, enabled per toolset. The default set (
core,groups,roles) is small; everything else is opt-in. - Least-privilege auth.
client_credentialswith a service account is the recommended grant; the password grant stays available. No credential defaults, so a missing setting fails fast. - Guardrails. Read-only mode, realm allowlist, write protection for the
masterrealm, and a preview-then-confirm: trueflow for destructive operations. - 4 guided prompts (onboarding, offboarding, security audit, failed-login investigation) and MCP resources for realms and users, with realm-name completion.
- Structured, paginated output with output schemas; secrets and credentials are never returned or logged.
- Works with Claude Desktop, Claude Code, VS Code, Cursor and any stdio MCP client. Requires Node.js 22 or newer.
How it works
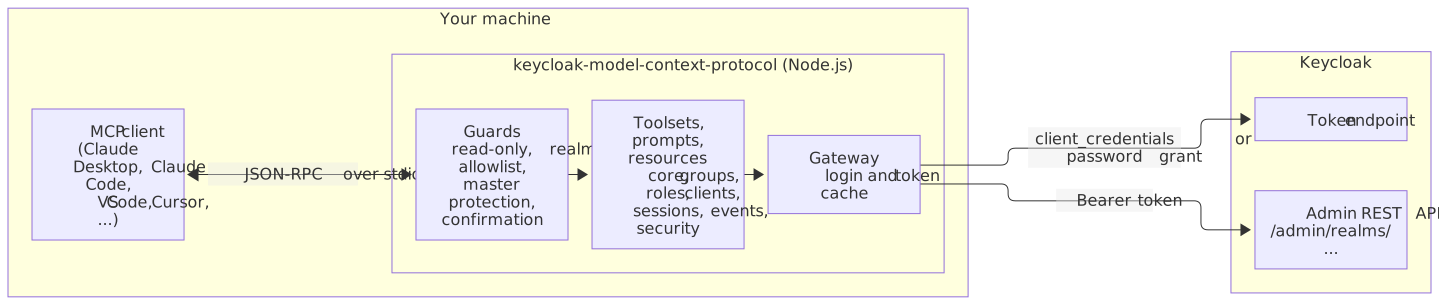
Your MCP client starts the server as a local child process and talks to it over stdio. Every tool call passes the guards, then goes through a single gateway that owns the Keycloak login and caches the access token.
What a destructive call looks like
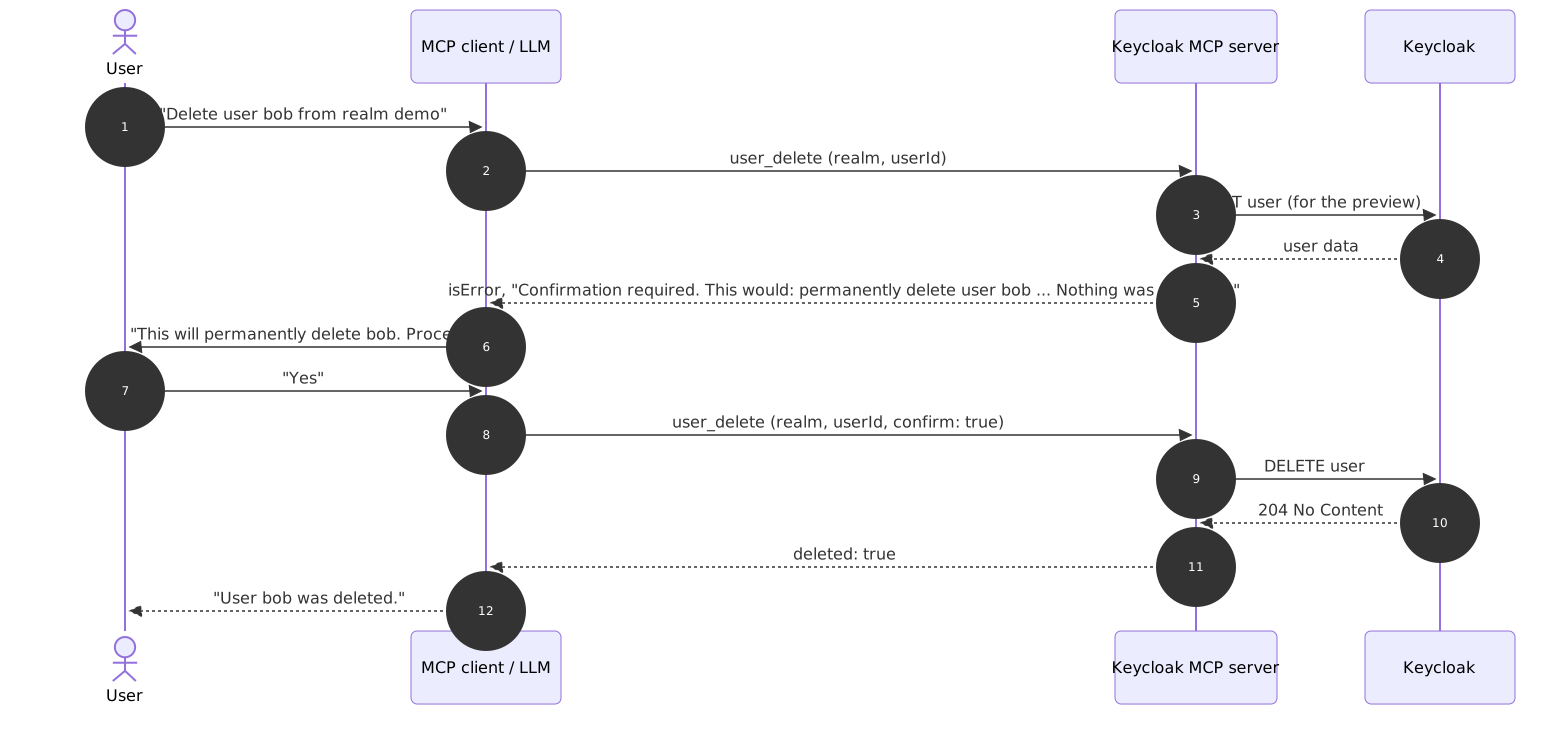
A destructive tool never acts on the first call. It returns a preview of what would happen and changes nothing. Only after you approve does the assistant repeat the call with confirm: true.
Quick start
Requirements: Node.js 22 or newer, a Keycloak server your machine can reach (tested with Keycloak 24.0 to 26.8), and an MCP client.
1. Prepare Keycloak (3 steps)
In the realm you want to administer (here demo):
- Create a client
mcp-adminwith Client authentication on and only Service accounts roles enabled (turn off Standard flow and Direct access grants). - Assign roles. On the client's Service accounts roles tab, assign client roles of
realm-management. For a first read-only trial:view-users,query-users,query-groups,view-realm. - Copy the secret from the client's Credentials tab.
Step-by-step instructions with Admin Console click paths, kcadm.sh commands and a local Docker Keycloak: docs/getting-started.md.
2. Configure your MCP client
Example for Claude Code (other clients: docs/clients.md):
claude mcp add --transport stdio \
  --env KEYCLOAK_URL=https://keycloak.example.com \
  --env KEYCLOAK_AUTH_REALM=demo \
  --env KEYCLOAK_CLIENT_ID=mcp-admin \
  --env KEYCLOAK_CLIENT_SECRET="$KEYCLOAK_CLIENT_SECRET" \
  keycloak -- npx -y keycloak-model-context-protocol
Or as JSON (Claude Desktop, claude_desktop_config.json):
{
  "mcpServers": {
    "keycloak": {
      "command": "npx",
      "args": ["-y", "keycloak-model-context-protocol"],
      "env": {
        "KEYCLOAK_URL": "https://keycloak.example.com",
        "KEYCLOAK_AUTH_REALM": "demo",
        "KEYCLOAK_CLIENT_ID": "mcp-admin",
        "KEYCLOAK_CLIENT_SECRET": "<client-secret>"
      }
    }
  }
}
3. Ask your first question
List the realms you can access, then show me the first 10 users of realm demo.
If you get an answer, you are done. If not, see docs/troubleshooting.md.
Configuration
All settings are environment variables. Only KEYCLOAK_URL and one set of credentials are required.
| Variable | Default | Purpose |
|---|---|---|
KEYCLOAK_URL | (required) | Base URL of the Keycloak server |
KEYCLOAK_AUTH_REALM | master | Realm where the login account or client lives |
KEYCLOAK_CLIENT_ID / KEYCLOAK_CLIENT_SECRET | none | client_credentials login (recommended) |
KEYCLOAK_USERNAME / KEYCLOAK_PASSWORD | none | Password grant login (client defaults to admin-cli) |
KEYCLOAK_GRANT_TYPE | auto | client_credentials or password; detected from what you set |
KEYCLOAK_MCP_TOOLSETS | core,groups,roles | Enabled toolsets, or all |
KEYCLOAK_MCP_READ_ONLY | false | Register read-only tools only |
KEYCLOAK_MCP_REALMS | all | Comma-separated allowlist of target realms |
KEYCLOAK_MCP_ALLOW_MASTER_WRITE | false | Allow write tools in the master realm |
KEYCLOAK_MCP_REQUIRE_CONFIRMATION | true | Destructive tools need confirm: true |
KEYCLOAK_MCP_TIMEOUT_MS | 30000 | HTTP timeout for Keycloak requests |
KEYCLOAK_MCP_LOG_LEVEL | info | debug, info, warn or error (stderr) |
Full reference with examples, validation rules and the tool-to-role matrix: docs/configuration.md.
Toolsets and tools
Tools are named <domain>_<verb>. Only the default toolsets are enabled unless you set KEYCLOAK_MCP_TOOLSETS. In read-only mode only tools of kind read are registered.
| Toolset | Default | Tools |
|---|---|---|
core | yes | realm_list, realm_get, user_search, user_get, user_create, user_update, user_delete (destructive), user_send_actions_email |
groups | yes | group_list, group_members_list, user_group_add, user_group_remove (destructive) |
roles | yes | role_list, user_roles_list, user_role_assign (confirmation for admin roles), user_role_revoke (destructive) |
clients | no | client_list, client_get |
sessions | no | user_sessions_list, user_logout (destructive) |
events | no | event_list, admin_event_list |
security | no | user_brute_force_status, user_brute_force_unlock |
Details for every tool (parameters, outputs, required roles): docs/tools-reference.md.
Prompts and resources
Prompts are guided workflows built on the tools. They appear in your client's prompt picker (in Claude Code as slash commands). The realm argument autocompletes.
| Prompt | What it does |
|---|---|
onboard_employee | Create a user, add groups and roles, send the welcome e-mail |
offboard_employee | Review, end sessions and disable a departing employee's account (does not delete) |
audit_realm_security | Read-only security review with prioritized findings |
investigate_failed_logins | Analyze failed logins and lockout status without changing anything |
Resources are read-only JSON documents, filtered by the same realm allowlist:
| URI | Content |
|---|---|
keycloak://realms | Names of accessible realms |
keycloak://realms/{realm} | Safe subset of the realm settings |
keycloak://realms/{realm}/security-summary | Brute-force, password policy, SSL, OTP, event flags, client exposure counts (no secrets) |
keycloak://realms/{realm}/users/{userId} | One user's basic fields (no attributes, no credentials) |
Security
- Least privilege first. Use a service-account client scoped to one realm with only the
realm-managementroles you need. A role matrix is in docs/configuration.md. - Destructive operations need confirmation (
KEYCLOAK_MCP_REQUIRE_CONFIRMATION=true), and granting administrative roles does too. - Blast-radius limits:
KEYCLOAK_MCP_READ_ONLY,KEYCLOAK_MCP_REALMS, and write protection formaster(off by default). - No secrets in output or logs. Credentials are masked on stderr; tools never return client secrets, user credentials or attributes.
- Prompt injection: treat names and descriptions coming from Keycloak as data. The shipped prompts say so explicitly; keep write tools disabled when you do not need them.
Threat model, hardening checklist and how to report a vulnerability: docs/security.md and SECURITY.md.
Example prompts
- "Which realms can you see? Show me the settings of realm
demo." - "Find all users in
demowhose e-mail ends with@example.comand who are disabled." - "Create user
jdoe(Jane Doe, jane@example.com) indemo, add her to groupengineeringand send her an e-mail to set a password." - "Who is in the group
ops, and which roles doesalicehave, including composite roles?" - "Run the
audit_realm_securityprompt fordemo." (needsclientsandeventstoolsets for the full audit) - "There were many failed logins last night. Investigate realm
demo." - "Offboard
bobindemo: end his sessions and disable the account."
Documentation
| Document | Content |
|---|---|
| docs/getting-started.md | Local Keycloak, service-account setup, first run, MCP Inspector |
| docs/configuration.md | Environment reference, role matrix, role profiles, TLS |
| docs/clients.md | Claude Desktop, Claude Code, VS Code, Cursor, generic clients |
| docs/tools-reference.md | Every tool in detail |
| docs/security.md | Threat model and hardening |
| docs/troubleshooting.md | Symptoms, causes, fixes |
| docs/architecture.md | Components, flows, design decisions |
| CHANGELOG.md | Release notes |
Upgrade from 0.x
Version 1.0 changes the defaults: credentials are required (no admin/admin fallback), destructive tools ask for confirmation, and the tools were renamed to <domain>_<verb> (for example create-user became user_create, delete-user became user_delete). The old KEYCLOAK_ADMIN and KEYCLOAK_ADMIN_PASSWORD variables still work but are deprecated. See the migration guide.
Contributing and license
Contributions are welcome. See CONTRIBUTING.md and the Code of Conduct. Released under the MIT License.
Reviews
No reviews yet
Be the first to review this server!
More Developer Tools MCP Servers
Rea
Freeby Morluto · Developer Tools
Reverse engineer anything from your terminal or agent with one CLI and MCP server.
Paperclip
Freeby Paperclipai · Developer Tools
Trending hip-hop artist momentum scores across four cultural dimensions.
Git
Freeby Modelcontextprotocol · Developer Tools
Read, search, and manipulate Git repositories programmatically
Fetch
Freeby Modelcontextprotocol · Developer Tools
Web content fetching and conversion for efficient LLM usage
Toleno
Freeby Toleno · Developer Tools
Toleno Network MCP Server — Manage your Toleno mining account with Claude AI using natural language.
MCP Marketplace
Freeby mcp-marketplace · Developer Tools
Search and install MCP servers from inside your AI client.