
Server data from the Official MCP Registry
Google Play reads and explicitly opted-in operations using your own local Google access.
About
Google Play reads and explicitly opted-in operations using your own local Google access.
Security Report
Valid MCP server (5 strong, 1 medium validity signals). 1 code issue detected. No known CVEs in dependencies. Package registry verified. Imported from the Official MCP Registry. 1 finding(s) downgraded by scanner intelligence.
8 files analyzed · 2 issues found
Security scores are indicators to help you make informed decisions, not guarantees. Always review permissions before connecting any MCP server.
Permissions Required
This plugin requests these system permissions. Most are normal for its category.
How to Install
Add this to your MCP configuration file:
{
  "mcpServers": {
    "io-github-pubship-pubship": {
      "args": [
        "pubship"
      ],
      "command": "uvx"
    }
  }
}Documentation
View on GitHubFrom the project's GitHub README.
PubShip
Google Play developer workflows, from your own computer. Inspect releases, understand reviews and reports, and prepare explicitly authorized changes from your MCP client.


Start locally
Use your own service account with permissions for your apps in Play Console. Keep its private JSON outside this repository. Grant only the permissions needed for your intended operations. Never paste credentials into an assistant conversation.
export GOOGLE_APPLICATION_CREDENTIALS=/absolute/private/path/service-account.json
export GOOGLE_PLAY_PACKAGES=com.example.app
uvx pubship
This starts the stdio server, which waits for an MCP client. For a credential-free installation check:
uvx pubship --check
The commands above install the published PyPI package. A source checkout may contain changes that are not yet published; after uv sync, use uv run pubship --check to check the local version.
Connect an assistant
Claude Code
claude mcp add --transport stdio pubship -- uvx pubship
Set the environment variables above in the shell launching your client. Restart the client after changing its environment.
Codex
codex mcp add pubship -- uvx pubship
Cursor and Gemini CLI
Client manifests in this repository declare the local service-account key path and package names. See client setup for configuration and the Gemini CLI installation command. For agent-assisted installation, read llms-install.md. Provide only the key file path, never its contents.
Generic MCP harness
Configure a stdio server with executable uvx, argument pubship, and your local environment. For clients that require explicit configuration:
{
  "mcpServers": {
    "pubship": {
      "command": "uvx",
      "args": ["pubship"],
      "env": {
        "GOOGLE_APPLICATION_CREDENTIALS": "/absolute/private/path/service-account.json",
        "GOOGLE_PLAY_PACKAGES": "com.example.app"
      }
    }
  }
}
Client configuration stays on your computer. Consult setup for alternate authentication modes, enabled APIs, reports and permission boundaries.
What can it do?
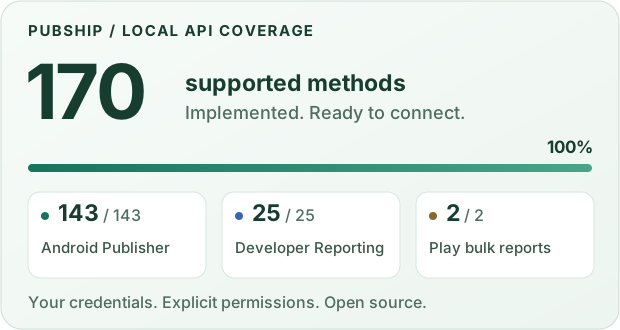
The pinned inventory contains 172 method definitions. 170 have implementations, one subscription-archive method is unsupported by Google, and voided-purchases access is deliberately disabled by project policy. Disabled operations cannot be called through local or self-host tools.
- Read releases, reviews, Android vitals and scoped bulk reports.
- Inspect catalog, subscription, product and account resources with separate sensitive-data grants.
- Prepare and review writes with explicit app/method permissions and single-use execution.
- Keep local file transfers bounded and separate publication from edit staging.
Reads are the default. Optional writes and sensitive reads require explicit configuration. Provider text is untrusted data. Missing data is not zero; a submitted change is not necessarily published. No operation count is a claim of live Google verification.
- Complete method inventory
- Related synthetic tests
- Edit lifecycle
- Purchase operations
- Artifact transfers
- Self-host configuration
Self-hosting for your own accounts
pubship-server retains the HTTP implementation for infrastructure you control. It refuses to start without PUBSHIP_SERVER_ALLOWED_EMAILS. Sign-in requires a signed Google ID token, a verified exact email match and nonce binding before any Google credentials are persisted. Removing an account from the allowlist invalidates its stored grants on next use. Legacy grants without verified identity must reconnect. Enrollment stays closed until the operator explicitly enables it.
There is no project-run Google-connected service. See the local-first decision and self-host setup.
Development
env -u GOOGLE_APPLICATION_CREDENTIALS uv sync --all-extras --group browser
env -u GOOGLE_APPLICATION_CREDENTIALS uv run pytest
env -u GOOGLE_APPLICATION_CREDENTIALS uv run ruff check .
env -u GOOGLE_APPLICATION_CREDENTIALS uv run ruff format --check .
env -u GOOGLE_APPLICATION_CREDENTIALS uv run python scripts/generate_catalog.py --check
env -u GOOGLE_APPLICATION_CREDENTIALS uv run python scripts/generate_verification.py --check
env -u GOOGLE_APPLICATION_CREDENTIALS uv run python scripts/distribution_metadata.py --check
env -u GOOGLE_APPLICATION_CREDENTIALS uv build
env -u GOOGLE_APPLICATION_CREDENTIALS uv run python scripts/check_artifacts.py
Tests use fake providers. Browser tests require installed Playwright engines; backup integration tests require age. Record unavailable platform checks honestly. See contribution policy, release process, and security reporting.
Intended use
PubShip helps developers automate their own Google Play distribution work. It runs on your computer or on infrastructure you control, with your own Google credentials and Play Console permissions. The PubShip project does not run a hosted service and never receives your credentials. Use it only for apps and developer accounts that you or your organization own, and follow Google's Play Developer API Terms. Hosted PubShip instances run by others are not provided or endorsed by the PubShip project.
PubShip is an independent open-source project and is not affiliated with, endorsed by, or sponsored by Google. Google, Google Play and Android are trademarks of Google LLC.
License
PubShip is free software under the GNU Affero General Public License v3.0 only (AGPL-3.0-only). Copyright (C) 2026 Denys Vorobyov. For other license terms, contact legal@pubship.dev.
Reviews
No reviews yet
Be the first to review this server!
More Developer Tools MCP Servers
Git
Freeby Modelcontextprotocol · Developer Tools
Read, search, and manipulate Git repositories programmatically
Fetch
Freeby Modelcontextprotocol · Developer Tools
Web content fetching and conversion for efficient LLM usage
Worldmonitor
Freeby Koala73 · Developer Tools
Live markets, conflicts, country risk, chokepoints, energy, and China decision signals. 89 tools.
Paperclip
Freeby Paperclipai · Developer Tools
Trending hip-hop artist momentum scores across four cultural dimensions.
Toleno
Freeby Toleno · Developer Tools
Toleno Network MCP Server — Manage your Toleno mining account with Claude AI using natural language.
mcp-creator-python
Freeby mcp-marketplace · Developer Tools
Create, build, and publish Python MCP servers to PyPI — conversationally.